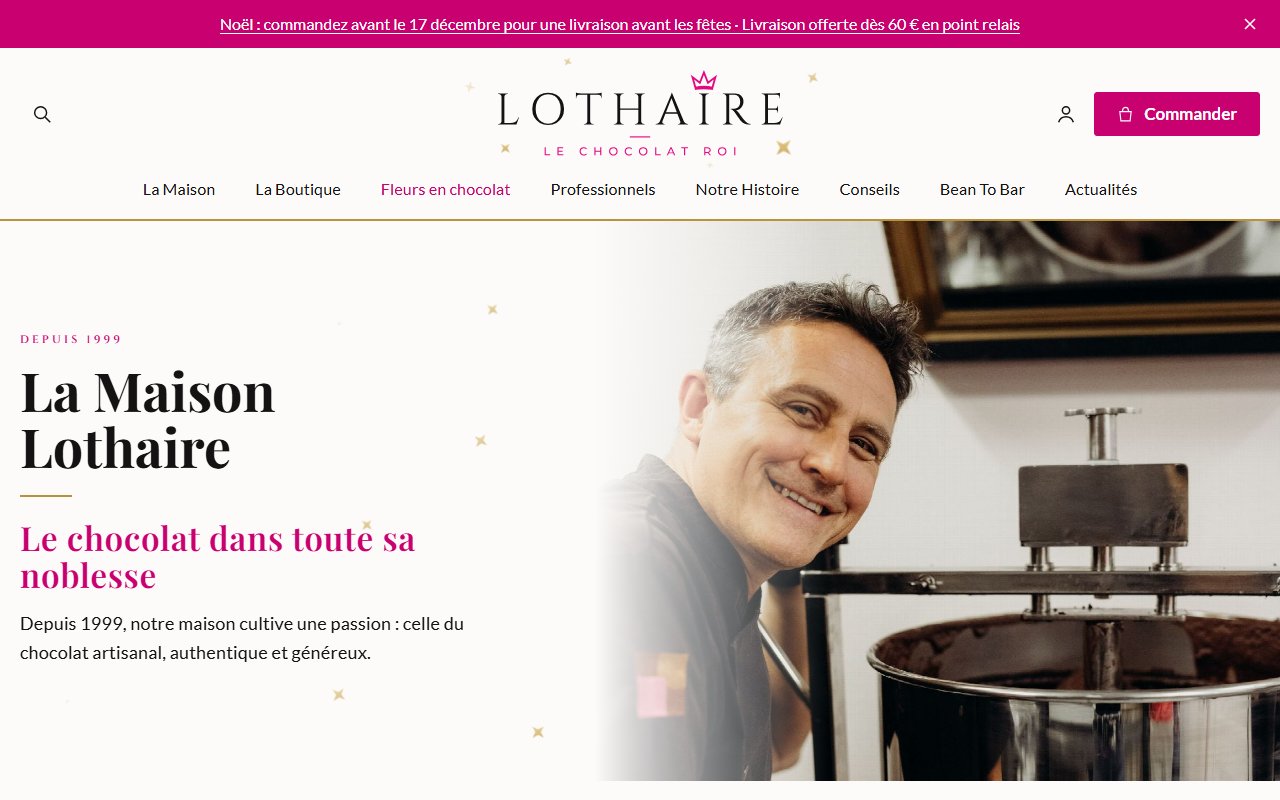
A hacked PrestaShop 1.7 store, secured and then rebuilt on PrestaShop 9 in 16 days: new design, Stripe, eight custom modules, every order and customer carried over, and search rankings kept.
The problem
Stéphane and Virginie Lothaire make their chocolate from bean to bar in their workshop in Vaudemange, near Reims. Virginie found me by asking ChatGPT. In October 2026, I discovered that their online store had been hacked: a malicious script displayed a fake credit card form. The flaw has been fixed and the customers concerned have been informed. The site was running on PrestaShop 1.7 and PHP 7.4, two versions that are no longer maintained, on hosting the chocolate maker had no control over. The first step was to secure it, then to rebuild a clean store without losing customers, orders or Google rankings, and before the Christmas sales.
What I did
- Cleaning and securing the hacked store, followed by a full audit (11 critical issues, 38 major ones) and the first fixes in production
- Migration from PrestaShop 1.7 to PrestaShop 9 with a replayable script: 104 products, 3,291 customers and 2,470 orders carried over, rehearsed several times before D-day
- New design in a Hummingbird child theme, chosen from three mock-ups
- Eight custom PrestaShop modules: trade area with reseller approval, accounting summary by VAT rate, order list, gift wrapping, seasonal banners, home page, anti-spam, cookie banner compliant with French CNIL rules
- Payment with Stripe (card, Apple Pay, Google Pay) instead of Up2pay; Mondial Relay, Colissimo and pick-up lockers
- 910 301 redirects tested one by one before going live
- Server in the chocolate maker’s name, illustrated back-office guide and year-round maintenance
Results
- Live on 19 November 2026, 16 days after signing, with 24 minutes of downtime
- The 68 pages that received clicks from Google kept their address or have a redirect
- A store on a maintained PrestaShop version, on a server monitored every week